 Innomerc
Choose your depth. Learn at your own pace.
Understand it
A password manager stores your account secrets in a protected vault so you do not need to memorize them all. You unlock the vault, then use a different generated password for each account. The vault itself deserves a strong master passphrase and careful recovery planning.
Autofill can help you notice the wrong website: if a familiar account is not offered, stop and check the address. Do not override that warning by copying a secret into a suspicious page. Autofill behavior depends on the product and its settings.
Under the hood
Managers typically encrypt vault content and derive protection from a master secret, device controls or both. Synchronization moves an encrypted representation between devices, but the exact trust and recovery model varies by product. Read that model before relying on it.
A browser integration matches saved entries with website origins or domains. It is a convenience with security implications, not a universal phishing detector. An unlocked endpoint, malicious extension or exposed clipboard can still compromise secrets.
Practitioner perspective
Evaluate managed deployment, enterprise recovery, audit events, vault sharing and administrator privileges. Recovery that bypasses a user’s master secret may be appropriate for a business, but changes who can recover sensitive data.
Offboarding must address shared secrets and active sessions as well as removal from a vault. Rotate credentials accessible to the departing user where necessary. Exported vault files are often highly sensitive and may be unencrypted; handle and delete them according to an approved process.
Picture the idea: one account, one password
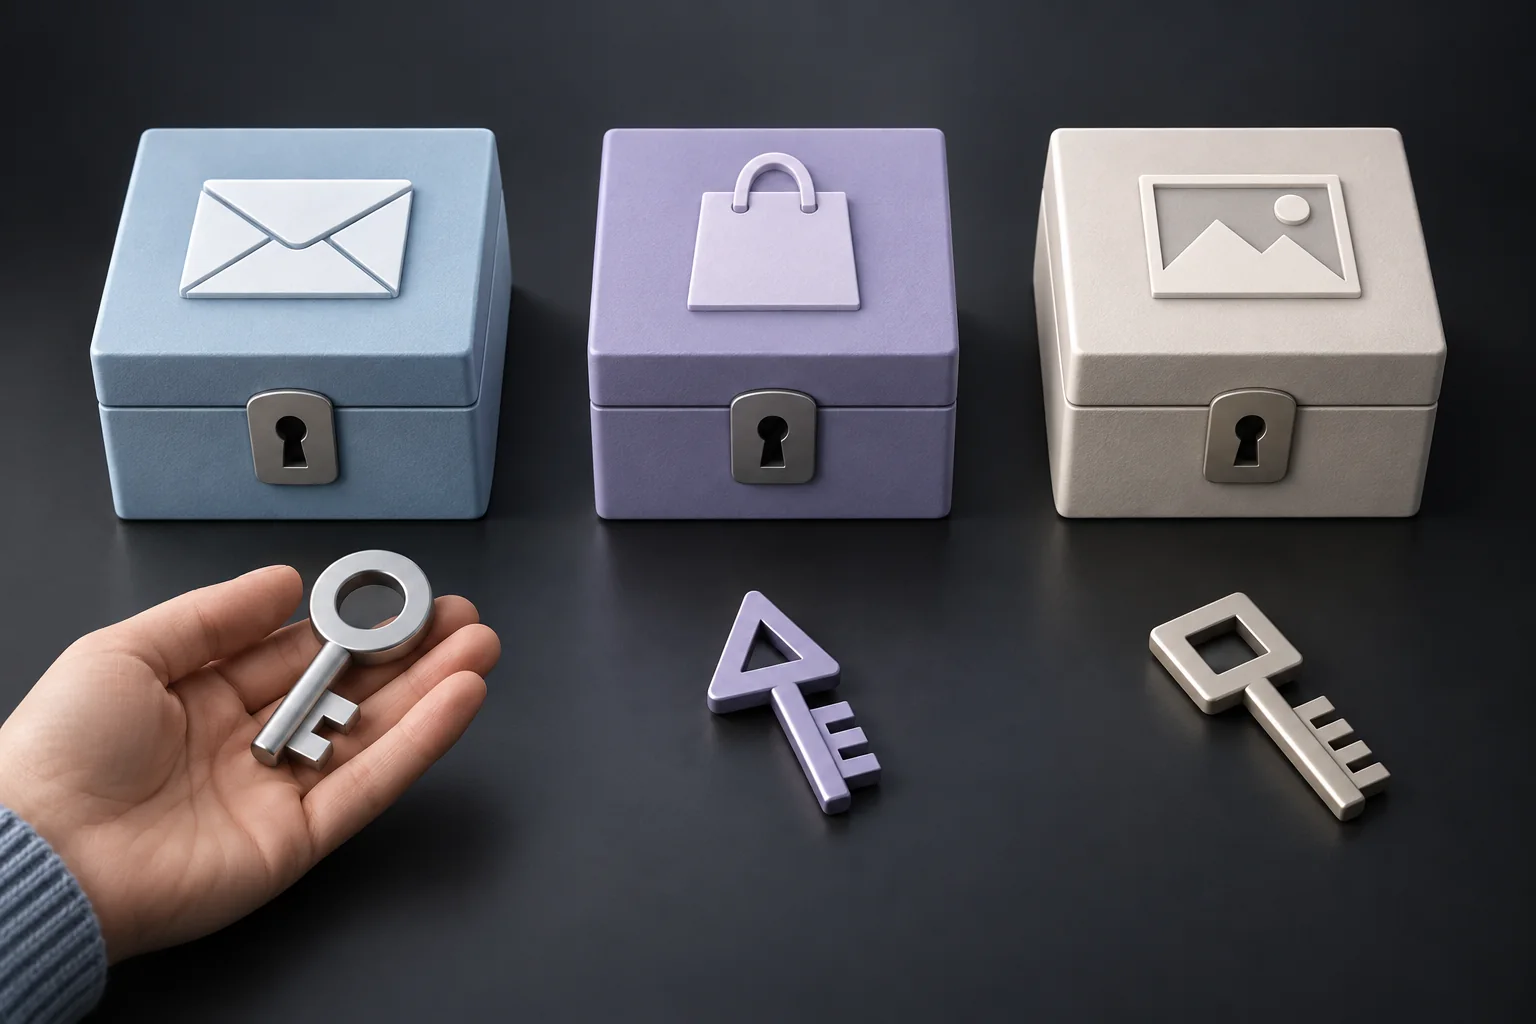
Different keys represent different passwords. A password exposed at one service should not unlock your other accounts. This illustrates uniqueness, not password strength or encryption.
Illustrated analogy · Select the image to enlargeWatch it work
A fictional, simplified model. Select a component to inspect it, or follow the steps in order.
Explore the system
Generate
Create a unique random password for the account.
Read every step without animation
Vault to website
- Generate. Create a unique random password for the account.
- Store. Save the secret in the protected vault.
- Check destination. Confirm the expected website before autofill.
- Sign in. Submit only to the intended service and complete MFA.
One account, one secret, released to the right destination.
What could go wrong
A lookalike sign-in page tries to receive an account password. The lesson shows the importance of checking the destination before releasing the secret.
What you can do
- Enable available MFA on the vault account.
- Keep the manager, browser and operating system updated.
- Prepare recovery instructions without leaving all recovery secrets beside an unlocked vault.
Common mistakes
- A password manager does not make a compromised device trustworthy.
- A vault export may not retain the vault’s encryption.
Check your understanding
Active recall: explain this idea in 30 seconds
A password manager stores your account secrets in a protected vault so you do not need to memorize them all. You unlock the vault, then use a different generated password for each account. The vault itself deserves a strong master passphrase and careful recovery planning.
Now give an example and name one limitation. Revisit the explanation if you get stuck.
Primary sources
Original explanations informed by these specifications and official resources. Source versions and lesson review are separate from product updates.
Content reviewed 2026-09-10. Read the editorial policy.