 Innomerc
Choose your depth. Learn at your own pace.
Understand it
A service secret is a credential software uses, such as an API key. Putting it in a shared code file can give other people the same access. Think of it like a key copied into every instruction booklet.
Use the organization’s approved secret-storage method. If a real secret is exposed, deleting the visible text is not enough: copied versions may still exist. Revoke or rotate the credential and investigate its use.
Under the hood
Limit a secret’s scope, lifetime and readers. Retrieve it through an approved mechanism and avoid leaking it into logs, build output or client-side bundles. Rotation must account for services still using the old value to prevent an uncontrolled outage.
Practitioner perspective
Define ownership, issuance, access auditing, rotation and emergency revocation for each credential class. Practise a staged replacement in an authorized environment and verify that the previous credential no longer works after the transition.
Secrets Management
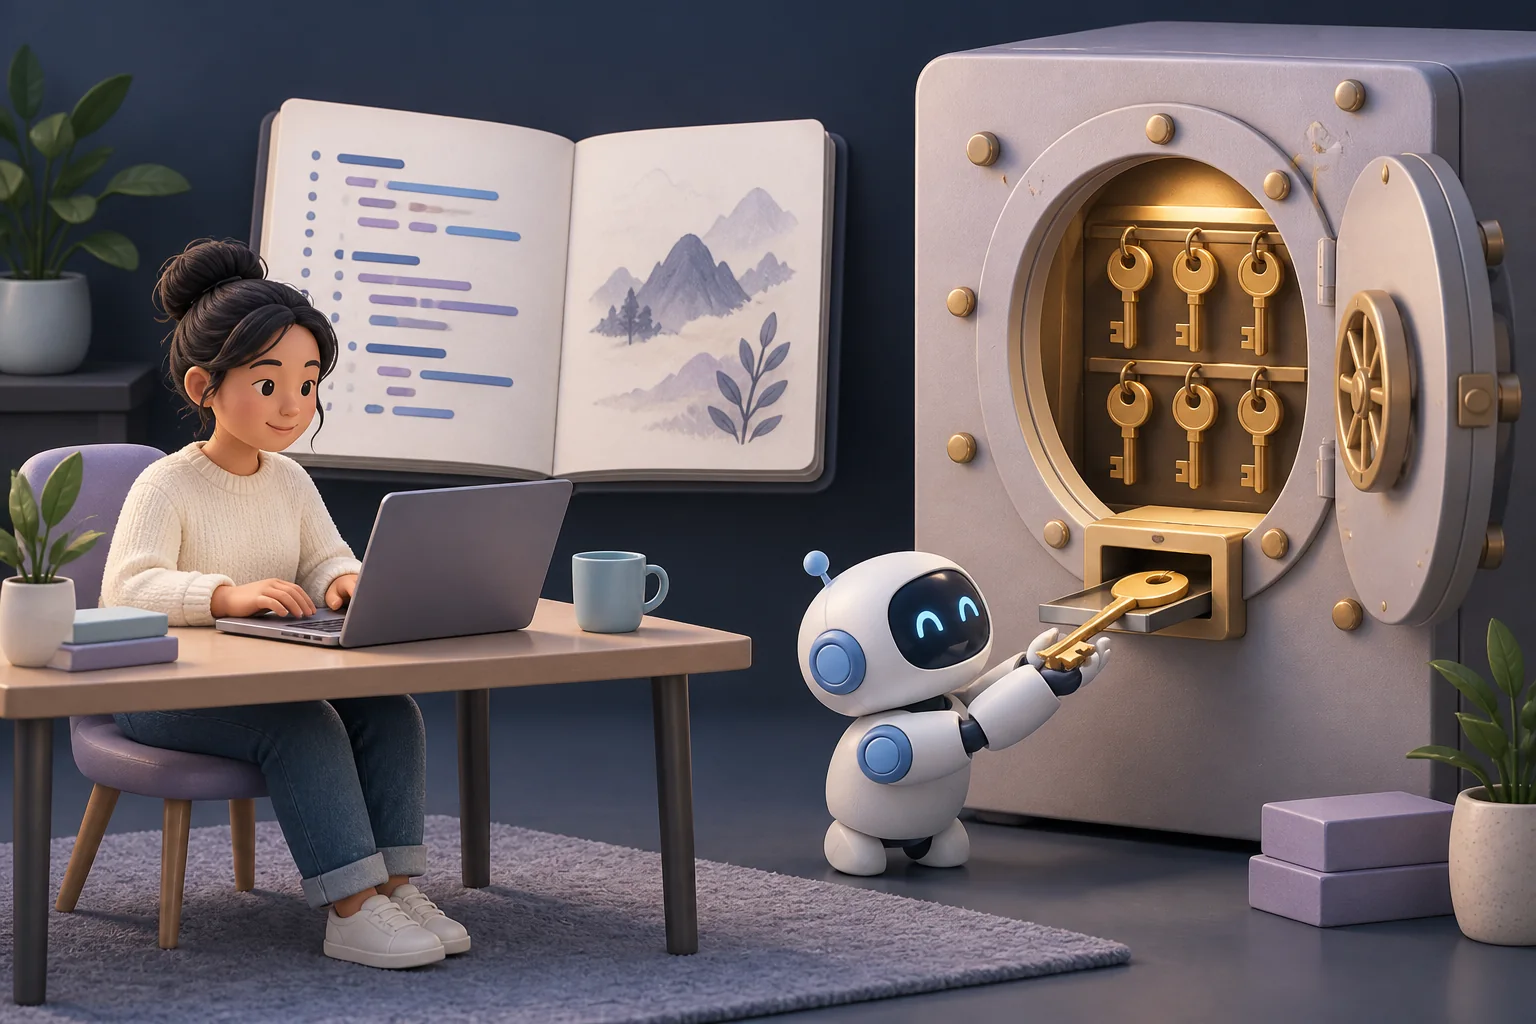
A service secret is a credential software uses, such as an API key. Putting it in a shared code file can give other people the same access. Think of it like a key copied into every instruction booklet.
Illustrated analogy · Select the image to enlargeWatch it work
A fictional, simplified model. Select a component to inspect it, or follow the steps in order.
Explore the system
Committed by mistake
An active key appears in a code change.
Read every step without animation
Credential exposed
- Committed by mistake. An active key appears in a code change.
- Revoke and replace. The owner follows the credential incident procedure.
- Review use. The team checks whether the exposed credential was used.
Invalidate the secret; do not rely on hiding its old location.
Planned rotation
- New credential. A replacement with necessary scope is issued.
- Update consumers. Authorized services are moved to the new credential.
- Retire old value. The old credential is revoked and the result checked.
Rotation includes checking both availability and revocation.
Attack view
A repository accidentally contains an active service credential.
Defender view
- Keep secrets in approved storage and grant only required access.
- Revoke exposed credentials and review access records rather than only deleting the file.
Common mistakes
- A private repository is not a substitute for secret management.
- Removing a line does not invalidate a copied credential.
Check your understanding
Active recall: explain this idea in 30 seconds
A service secret is a credential software uses, such as an API key. Putting it in a shared code file can give other people the same access. Think of it like a key copied into every instruction booklet.
Now give an example and name one limitation. Revisit the explanation if you get stuck.
Primary sources
Original explanations informed by these specifications and official resources. Source versions and lesson review are separate from product updates.
Content reviewed 2026-09-11. Read the editorial policy.