
Simple: everyday language, with no technical background needed.
Understand it
A visitor needs access to the meeting room, not every office. Least privilege applies this idea to accounts: give the access needed for the current task. Reading a document, editing it and changing who can read it are different powers.
A temporary helper may need to view a folder for one week. Choose the correct role, set an end point if supported, and check that access has been removed when the task ends.
Under the hood
Effective access can come from roles, groups, direct grants and inherited policy. Review the combined permissions. Use separate privileged identities or elevation when appropriate, and avoid giving normal everyday sessions unnecessary administrative capabilities.
Practitioner perspective
Assign access owners and review joiner, mover and leaver changes. Measure whether permissions match tasks and whether revocation actually works. Emergency access needs a controlled process and review; reducing privileges without understanding dependencies can also disrupt essential work.
Least Privilege
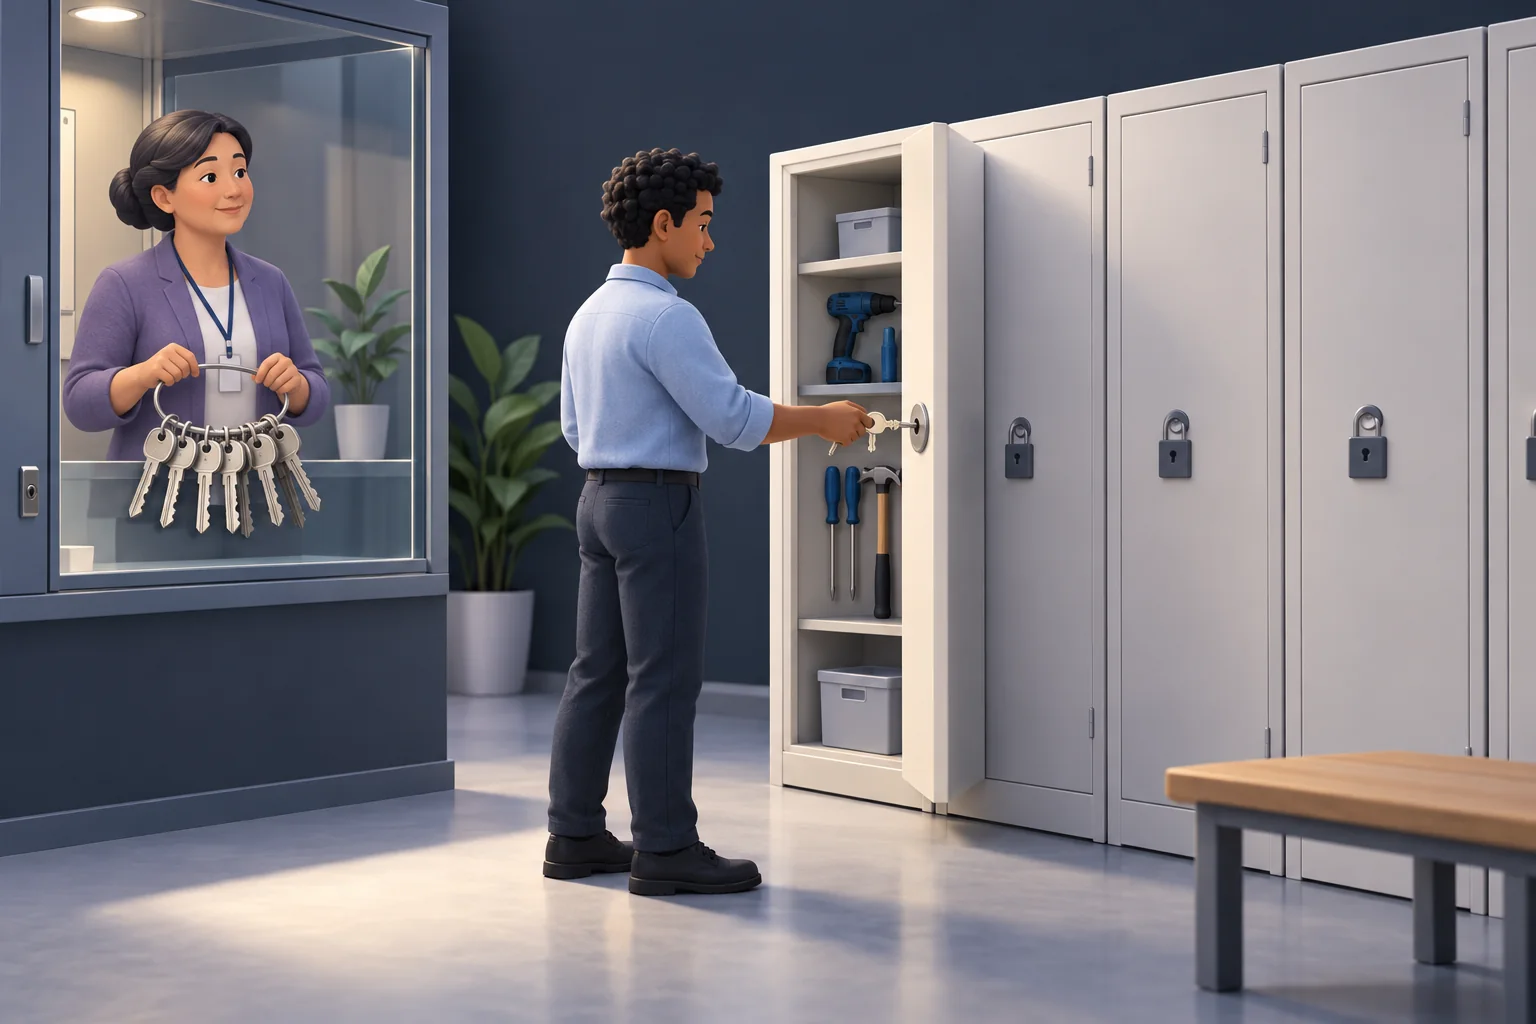
A visitor needs access to the meeting room, not every office. Least privilege applies this idea to accounts: give the access needed for the current task. Reading a document, editing it and changing who can read it are different powers.
Illustrated analogy · Select the image to enlargeWatch it work
A fictional, simplified model. Select a component to inspect it, or follow the steps in order.
A link is a route. Permission opens the file.
Example: Mira shares a fictional meeting agenda. Compare a public link with a named invitation.
Anyone with the link
The link can travel beyond the first person who receives it.
How to use this example
Select Next step to read at your own pace, or Animate step to watch one exchange. Nothing advances until you choose.
What it means
Everyday example
State in this scenario
Inspect components & read every step
- Mira
The fictional owner sharing a file in this example.
Example: Mira decides who may read the meeting agenda.
- Shared file
A document whose access is controlled by sharing settings.
Example: An agenda may be restricted to named readers or available to anyone with its link.
- New reader
Someone attempting to open a shared document.
Example: Receiving a forwarded link does not automatically grant access to a restricted file.
Anyone with the link
The link can travel beyond the first person who receives it.
- Mira Shared file: Broad access. Mira allows anyone holding the link to read the agenda.
- New reader Shared file: Forwarded link. Another person opens a forwarded copy of the link.
- Shared file New reader: File returned. The broad permission allows this reader to receive the file.
Named readers only
Forwarding a link does not add a person to a restricted access list.
- Mira Shared file: Named invitation. Mira grants viewing access only to her intended reviewer.
- New reader Shared file: Forwarded link. A different person requests the same restricted file.
- Shared file New reader: Access denied. The service checks identity and does not send the file.
Fictional teaching trace. One moving dot represents an exchange, not a measured network capture.
Open the detailed lesson walkthrough
Explore the system
Task
A helper only needs to read a draft.
Read every step without animation
Broad access
- Task. A helper only needs to read a draft.
- Admin role. The account receives unnecessary control.
- Larger impact. Misuse can affect much more than the draft.
Extra permissions expand the possible harm.
Task-based access
- Task. Identify what the helper needs to do.
- Read role. Grant access to the needed draft only.
- Remove access. Revoke the grant when the work ends.
Match both the scope and duration to the task.
Attack view
A compromised everyday account has unnecessary administrative rights and can change other users’ access.
Defender view
- Grant a role that matches the task and review the effective permissions.
- Remove unneeded access when the task or role changes.
Common mistakes
- Being signed in does not mean every action should be allowed.
- A role name alone does not prove its actual permissions are limited.
Check your understanding
Active recall: explain this idea in 30 seconds
A visitor needs access to the meeting room, not every office. Least privilege applies this idea to accounts: give the access needed for the current task. Reading a document, editing it and changing who can read it are different powers.
Now give an example and name one limitation. Revisit the explanation if you get stuck.
Primary sources
Original explanations informed by these specifications and official resources. Source versions and lesson review are separate from product updates.
Content reviewed 2026-09-10. Read the editorial policy.