
Simple: everyday language, with no technical background needed.
Understand it
Cryptographic failures leave information insufficiently protected because encryption, key handling or related security choices are missing or wrong.
Cedar encrypts a backup but stores its decryption key beside it with the same access permissions. Anyone who obtains both can recover the protected data.
Under the hood
Choose established libraries and protocols, appropriate authenticated encryption and cryptographically suitable randomness. Password storage needs a password-hashing design, not ordinary reversible encryption.
Practitioner perspective
Map where plaintext exists and who can use the keys. Plan rotation, recovery and destruction. A strong algorithm does not compensate for a leaked key, incorrect nonce handling or a service that returns decrypted data to an unauthorized caller.
Encryption
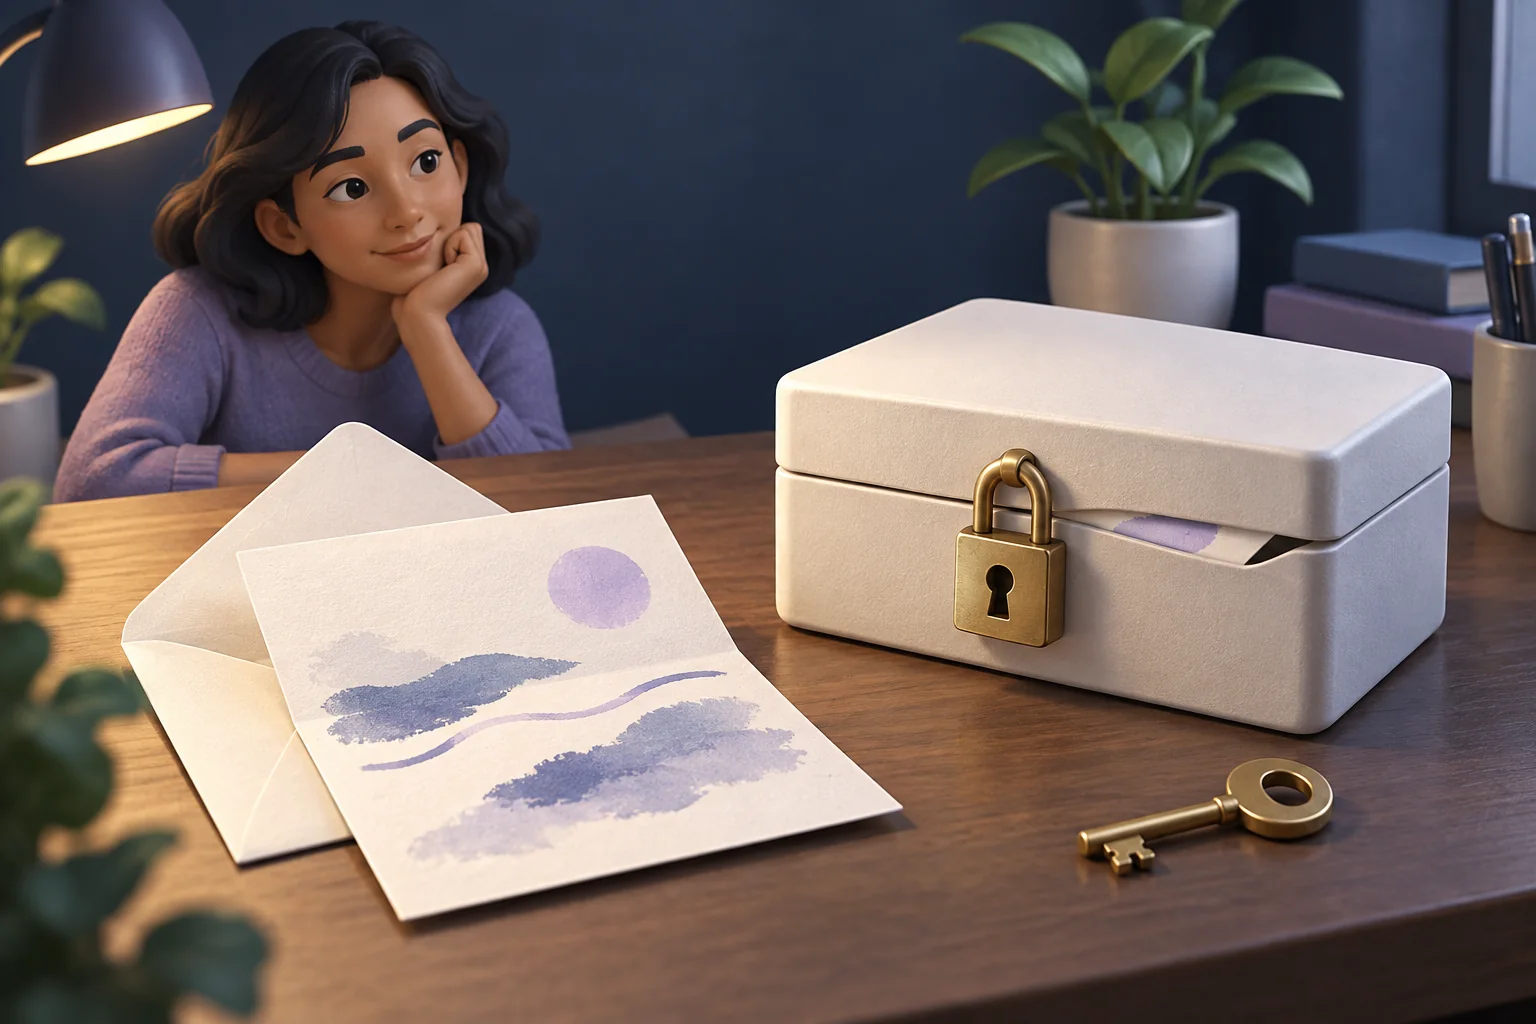
Cryptographic failures leave information insufficiently protected because encryption, key handling or related security choices are missing or wrong.
Illustrated analogy · Select the image to enlargeWatch it work
A fictional, simplified model. Select a component to inspect it, or follow the steps in order.
Explore the system
Sensitive backup
Cedar encrypts a backup but stores its decryption key beside it with the same access permissions. Anyone who obtains both can recover the protected data.
Read every step without animation
Failure path
- Sensitive backup. Cedar encrypts a backup but stores its decryption key beside it with the same access permissions. Anyone who obtains both can recover the protected data.
- Key beside data. Cryptographic failures leave information insufficiently protected because encryption, key handling or related security choices are missing or wrong.
- Both exposed. Encryption does not remove the need for authorization.
The intended security boundary is not enforced.
Defensive path
- Restricted key service. Separate key access from data access and minimize retained sensitive data.
- Authorized use. Choose established libraries and protocols, appropriate authenticated encryption and cryptographically suitable randomness. Password storage needs a password-hashing design, not ordinary reversible encryption.
- Protected backup. Map where plaintext exists and who can use the keys. Plan rotation, recovery and destruction. A strong algorithm does not compensate for a leaked key, incorrect nonce handling or a service that returns decrypted data to an unauthorized caller.
The improved path addresses the specific failure; verify it in your environment.
Attack view
Cedar encrypts a backup but stores its decryption key beside it with the same access permissions. Anyone who obtains both can recover the protected data.
Defender view
- Separate key access from data access and minimize retained sensitive data.
- Verify the expected allowed and denied outcomes in a controlled environment.
Common mistakes
- Encryption does not remove the need for authorization.
- Keeping the decryption key beside exposed ciphertext undermines the intended separation.
Check your understanding
Active recall: explain this idea in 30 seconds
Cryptographic failures leave information insufficiently protected because encryption, key handling or related security choices are missing or wrong.
Now give an example and name one limitation. Revisit the explanation if you get stuck.
Primary sources
Original explanations informed by these specifications and official resources. Source versions and lesson review are separate from product updates.
Content reviewed 2026-09-10. Framework reference: OWASP Top 10 2025. Read the editorial policy.