 Innomerc
Choose your depth. Learn at your own pace.
Understand it
TLS creates a protected channel between endpoints. The client checks evidence of the server’s identity and the two sides establish keys to protect their communication. The certificate is part of that identity check; it is not the encryption for the entire conversation.
A browser normally checks that the certificate covers the requested hostname, is within its validity period and chains to a trusted authority. Do not bypass a browser’s certificate warning to complete a sign-in. The warning means an expected identity check did not succeed.
Under the hood
In a typical TLS 1.3 handshake, the client offers parameters and a key share. The server chooses compatible parameters and provides its share. Both derive handshake secrets; the server’s certificate and signature authenticate the exchange before application traffic is accepted.
Public-key operations authenticate and establish secrets; symmetric authenticated encryption protects records efficiently. Session resumption can shorten later handshakes. Optional 0-RTT data has replay considerations and is not suitable for every application operation.
Practitioner perspective
Inventory supported protocol versions, certificates, key custody and termination points. TLS policy belongs to both the client and server. Automated issuance does not remove the need to monitor renewals, hostname coverage and expiry.
Distinguish certificate validation failure from protocol negotiation failure and application failure after a successful handshake. For 0-RTT, reason about replay-safe operations rather than assuming transport encryption implies exactly-once processing. Mutual TLS adds client authentication but still needs authorization.
TLS
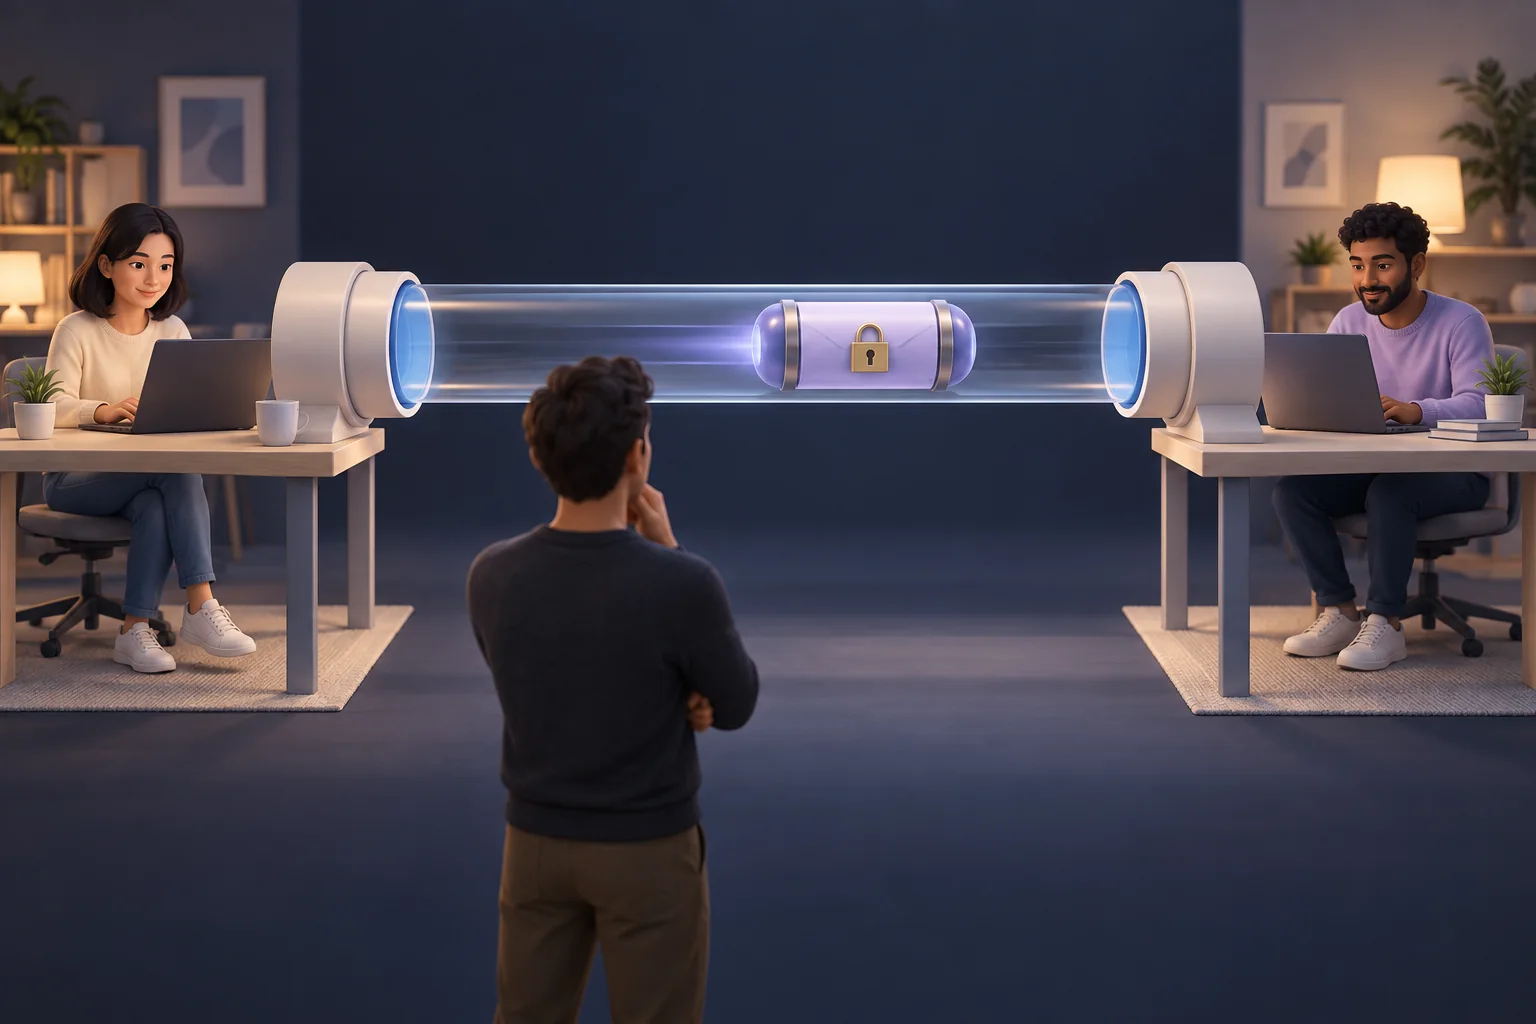
TLS creates a protected channel between endpoints. The client checks evidence of the server’s identity and the two sides establish keys to protect their communication. The certificate is part of that identity check; it is not the encryption for the entire conversation.
Illustrated analogy · Select the image to enlargeWatch it work
A fictional, simplified model. Select a component to inspect it, or follow the steps in order.
Explore the system
ClientHello
The client sends supported parameters and a key share.
Read every step without animation
TLS 1.3 handshake
- ClientHello. The client sends supported parameters and a key share.
- ServerHello. The server selects parameters and contributes its key share.
- Identity evidence. The server proves possession of the key associated with its certificate.
- Client validation. The client verifies the expected identity and handshake.
- Protected records. Both sides use derived traffic keys for authenticated encryption.
The simplified handshake establishes a protected channel, not application authorization.
Attack view
An intermediary presenting the wrong identity should fail certificate validation. A compromised trusted endpoint, stolen session or unsafe application remains outside that single protection.
Defender view
- Use supported TLS libraries and current configuration guidance.
- Automate certificate renewal and monitor failure before expiry.
- Protect private keys and define trust boundaries at load balancers and proxies.
Common mistakes
- The certificate does not itself encrypt every application byte.
- TLS does not hide data from the endpoint that terminates it.
Check your understanding
Active recall: explain this idea in 30 seconds
TLS creates a protected channel between endpoints. The client checks evidence of the server’s identity and the two sides establish keys to protect their communication. The certificate is part of that identity check; it is not the encryption for the entire conversation.
Now give an example and name one limitation. Revisit the explanation if you get stuck.
Primary sources
Original explanations informed by these specifications and official resources. Source versions and lesson review are separate from product updates.
Content reviewed 2026-09-10. Read the editorial policy.