 Innomerc
One useful thing to do today
Verify the network name and disable automatic joining of unknown networks.
More everyday safety lessonsChoose your depth. Learn at your own pace.
Understand it
Public WiFi means sharing network access with a provider and potentially unfamiliar devices. A familiar network name is not proof of who operates it. Verify the network with the venue and avoid entering account credentials into unexpected captive-portal pages.
Modern HTTPS protects the content of a properly validated connection from ordinary network observers. That is useful protection, but it does not make a fake login page genuine or fix an outdated device. For sensitive work, use a connection and device you trust.
Under the hood
A local observer may see connection metadata even when content is encrypted. Exactly what remains visible depends on DNS transport, TLS features, proxies and the application. Do not assume that every app correctly protects all of its traffic.
A VPN creates a protected tunnel to its provider or organization. It changes which intermediary you trust. The local network sees the tunnel connection rather than the destinations and content carried inside it; the VPN tunnel ends at the VPN provider or organization. HTTPS is still needed to protect application traffic onward to the destination. It does not inherently prevent phishing, malicious downloads or tracking by the destination service.
Practitioner perspective
For managed devices, define network profiles, host firewall rules, sharing settings and access policy. Treat captive portals as untrusted input. Avoid interpreting “connected to VPN” as proof of endpoint health or complete tunnel coverage.
Incident analysis should distinguish local network exposure, destination compromise and endpoint compromise. Certificate warnings deserve investigation; bypassing them can remove the identity check that transport protection depends on.
TLS
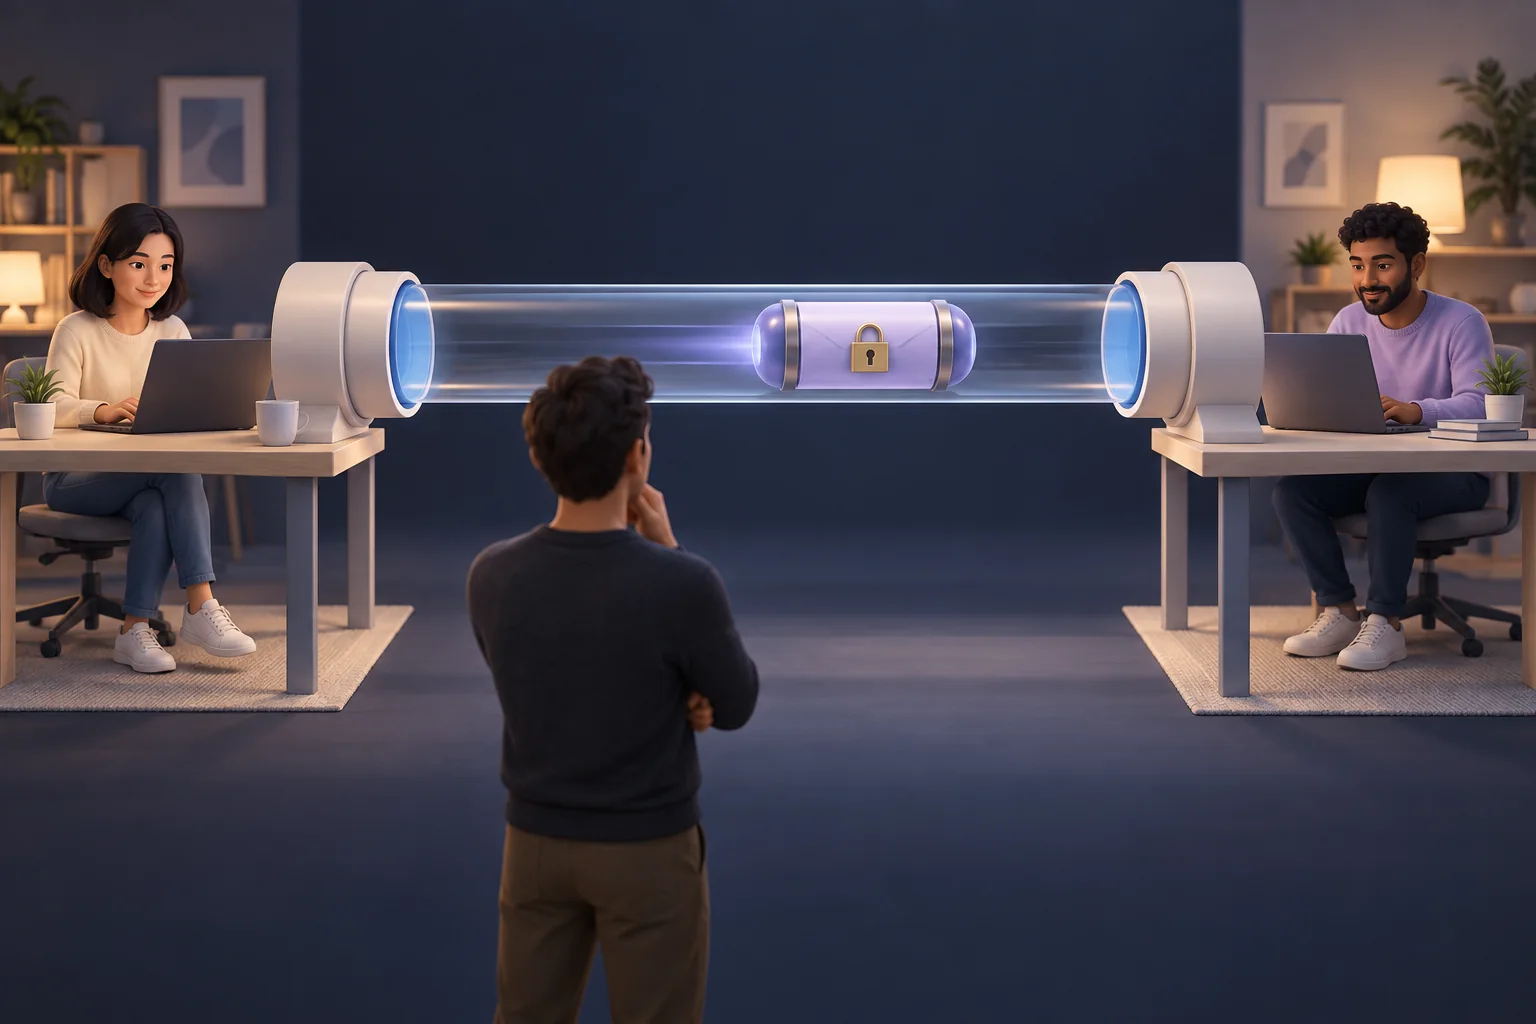
Public WiFi means sharing network access with a provider and potentially unfamiliar devices. A familiar network name is not proof of who operates it. Verify the network with the venue and avoid entering account credentials into unexpected captive-portal pages.
Illustrated analogy · Select the image to enlargeWatch it work
A fictional, simplified model. Select a component to inspect it, or follow the steps in order.
Explore the system
Your device
The browser requests the expected website.
Read every step without animation
HTTPS on shared WiFi
- Your device. The browser requests the expected website.
- Shared network. The network carries protected traffic and can observe some metadata.
- TLS endpoint. The intended service decrypts and processes the HTTP request.
The content is protected in transit when TLS is correctly validated.
VPN tunnel
- Your device. Traffic covered by the VPN enters the tunnel.
- VPN endpoint. The VPN operator terminates the tunnel and forwards traffic.
- Destination. HTTPS still protects the application connection to its endpoint.
The tunnel changes the network trust boundary; HTTPS still matters.
What could go wrong
A rogue access point uses a familiar-looking name. The visual focuses on verifying the connection and preserving HTTPS checks, not on bypassing encryption.
What you can do
- Verify the network name and disable automatic joining of unknown networks.
- Keep file sharing restricted and software updated.
- Do not bypass certificate warnings; consider a trusted mobile connection when uncertain.
Common mistakes
- Public WiFi does not automatically reveal all HTTPS content.
- A VPN provider is another trust relationship, not a universal safety switch.
Check your understanding
Active recall: explain this idea in 30 seconds
Public WiFi means sharing network access with a provider and potentially unfamiliar devices. A familiar network name is not proof of who operates it. Verify the network with the venue and avoid entering account credentials into unexpected captive-portal pages.
Now give an example and name one limitation. Revisit the explanation if you get stuck.
Primary sources
Original explanations informed by these specifications and official resources. Source versions and lesson review are separate from product updates.
Content reviewed 2026-09-10. Read the editorial policy.