
Simple: everyday language, with no technical background needed.
Understand it
A cryptographic hash turns data into a fixed-length digest. Think of it as a fingerprint for comparing the exact bytes. A small change normally gives a very different result. You do not decrypt a digest to get the original file back.
Suppose a publisher gives a file and its expected hash. Calculate your file’s digest and compare. This only helps if the expected value came from a trusted source; a replaced file and replaced checksum can agree.
Under the hood
Cryptographic hashes are designed to resist finding matching inputs or recovering an input from its digest. Collisions must exist because the output space is finite. General-purpose fast hashing alone is unsuitable for password storage, which needs a dedicated salted password-hashing scheme.
Practitioner perspective
Separate accidental-corruption checks from authenticity claims. Establish trust in the reference digest or use a verified digital signature. Record the algorithm and exact artifact version in evidence; matching hashes do not prove that a file is safe to execute.
Hashing
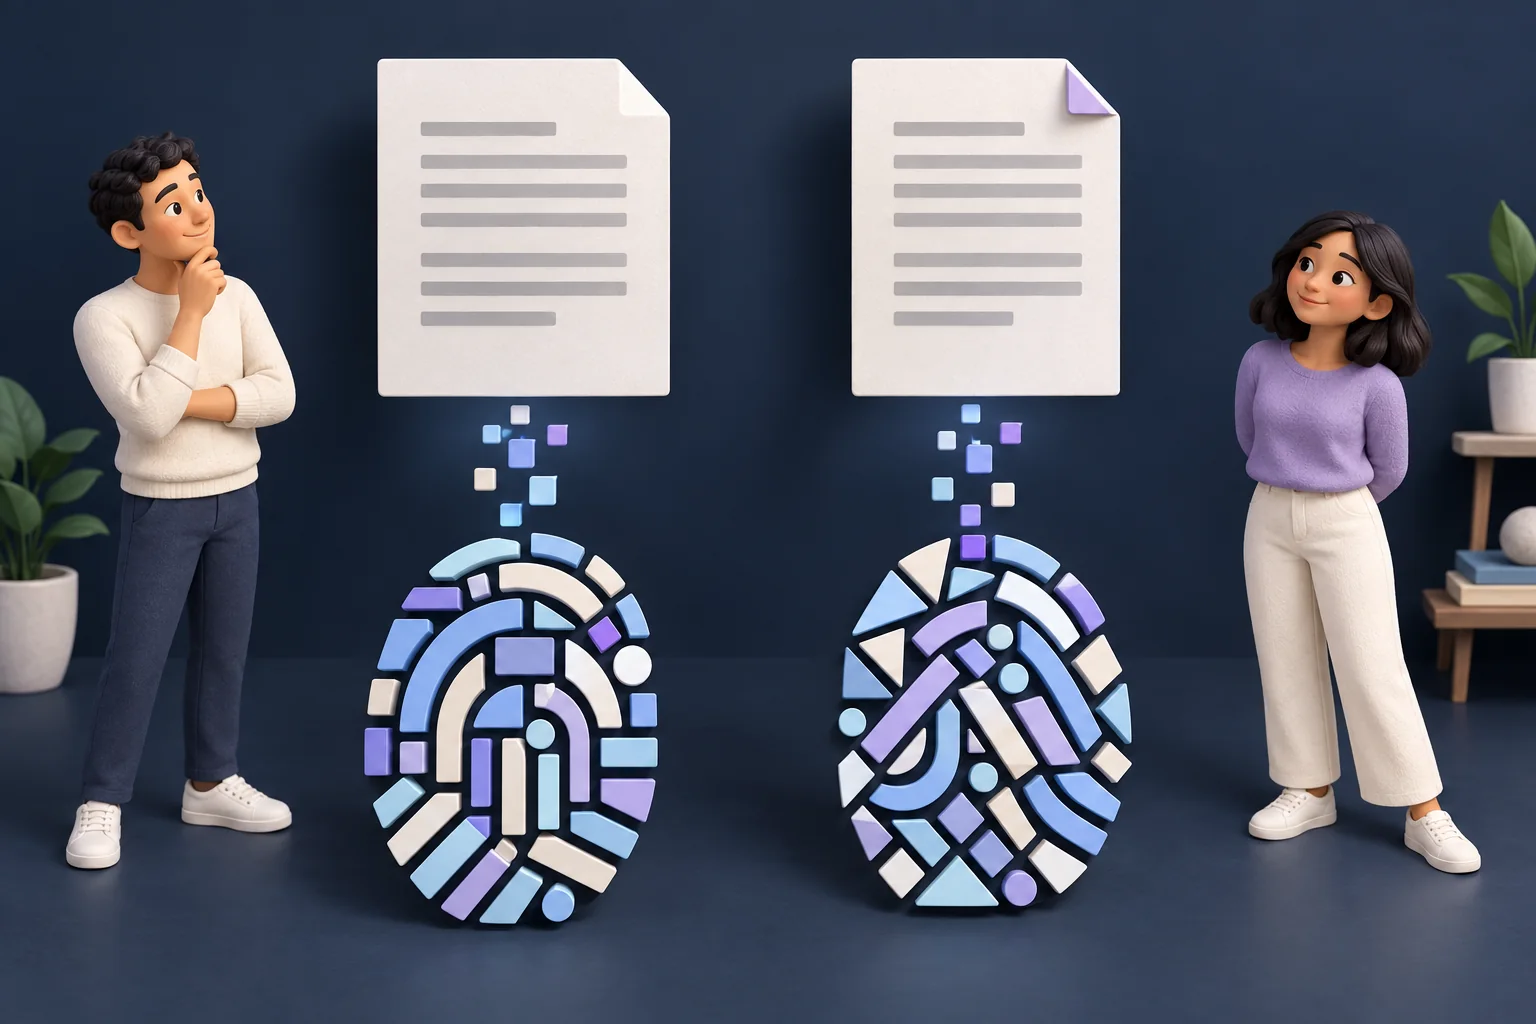
A cryptographic hash turns data into a fixed-length digest. Think of it as a fingerprint for comparing the exact bytes. A small change normally gives a very different result. You do not decrypt a digest to get the original file back.
Illustrated analogy · Select the image to enlargeWatch it work
A fictional, simplified model. Select a component to inspect it, or follow the steps in order.
A small change produces a different fingerprint.
Example: compare a downloaded file with a hash obtained from a trusted source. A hash does not hide the file.
Matching file
A matching hash is useful only when the expected value comes from a trustworthy source.
How to use this example
Select Next step to read at your own pace, or Animate step to watch one exchange. Nothing advances until you choose.
What it means
Everyday example
State in this scenario
Inspect components & read every step
- You
The person making the decision in this fictional example.
Example: You decide whether to share information, approve a request or check it first.
- Check or transform
A hash calculation and comparison. This checks a fingerprint; it does not encrypt the file.
Example: Compare the downloaded file’s hash with a value from a trusted source.
- Result
The outcome produced by the operation in this example.
Example: Read the current state and the step explanation to see what succeeded or failed.
Matching file
A matching hash is useful only when the expected value comes from a trustworthy source.
- You Check or transform: Hash the download. A hash function calculates a fixed-length value from the downloaded file.
- Check or transform Result: Compare trusted value. The values match in this example. This supports integrity relative to that trusted reference, not a guarantee that the file is harmless.
Changed file
A different hash means the bytes do not match the expected file.
- You Check or transform: Hash changed bytes. The same function hashes a file whose contents have changed.
- Check or transform Result: Mismatch found. The calculated value differs from the trusted reference. Do not treat this download as the expected file.
Fictional teaching trace. One moving dot represents an exchange, not a measured network capture.
Open the detailed lesson walkthrough
Explore the system
Original
A trusted reference digest identifies the expected bytes.
Read every step without animation
Accidental change
- Original. A trusted reference digest identifies the expected bytes.
- Changed file. The downloaded file has different bytes.
- Mismatch. The calculated digest does not match the reference.
Do not use a mismatching artifact until the cause is understood.
Untrusted reference
- Wrong file. A malicious file is offered.
- Matching digest. Its distributor supplies a matching checksum.
- Trust missing. The match does not prove authenticity.
The source of the reference matters.
Attack view
A malicious download is accompanied by the attacker’s own matching checksum.
Defender view
- Obtain the reference digest through a trusted independent or authenticated source.
- Use dedicated password-hashing libraries for credentials rather than inventing a scheme.
Common mistakes
- Hashing is not reversible encryption.
- A matching checksum does not prove software is harmless.
Check your understanding
Active recall: explain this idea in 30 seconds
A cryptographic hash turns data into a fixed-length digest. Think of it as a fingerprint for comparing the exact bytes. A small change normally gives a very different result. You do not decrypt a digest to get the original file back.
Now give an example and name one limitation. Revisit the explanation if you get stuck.
Primary sources
Original explanations informed by these specifications and official resources. Source versions and lesson review are separate from product updates.
Content reviewed 2026-09-10. Read the editorial policy.