 Innomerc
Choose your depth. Learn at your own pace.
Understand it
Incident response is a coordinated way to handle a suspected or confirmed security event. Reporting early helps the team assess what happened. You do not need to prove the whole incident before asking the right team for help.
At work, follow the organization’s response process. Record what you observed and avoid deleting evidence or experimenting on the affected system. Containment, investigation, communication and recovery need coordinated decisions.
Under the hood
Triage identifies scope and urgency; containment reduces ongoing harm. Evidence collection, eradication and recovery can overlap rather than forming a perfect one-way sequence. Use timestamps with time zones and preserve relevant originals under the organization’s procedures.
Practitioner perspective
NIST SP 800-61 Rev. 3 integrates response into CSF 2.0 risk management. Preparation spans governance and protection; detection, response and recovery rely on those capabilities. Establish authority for isolation, communications and external notifications; evaluate local legal requirements separately.
Incident Response
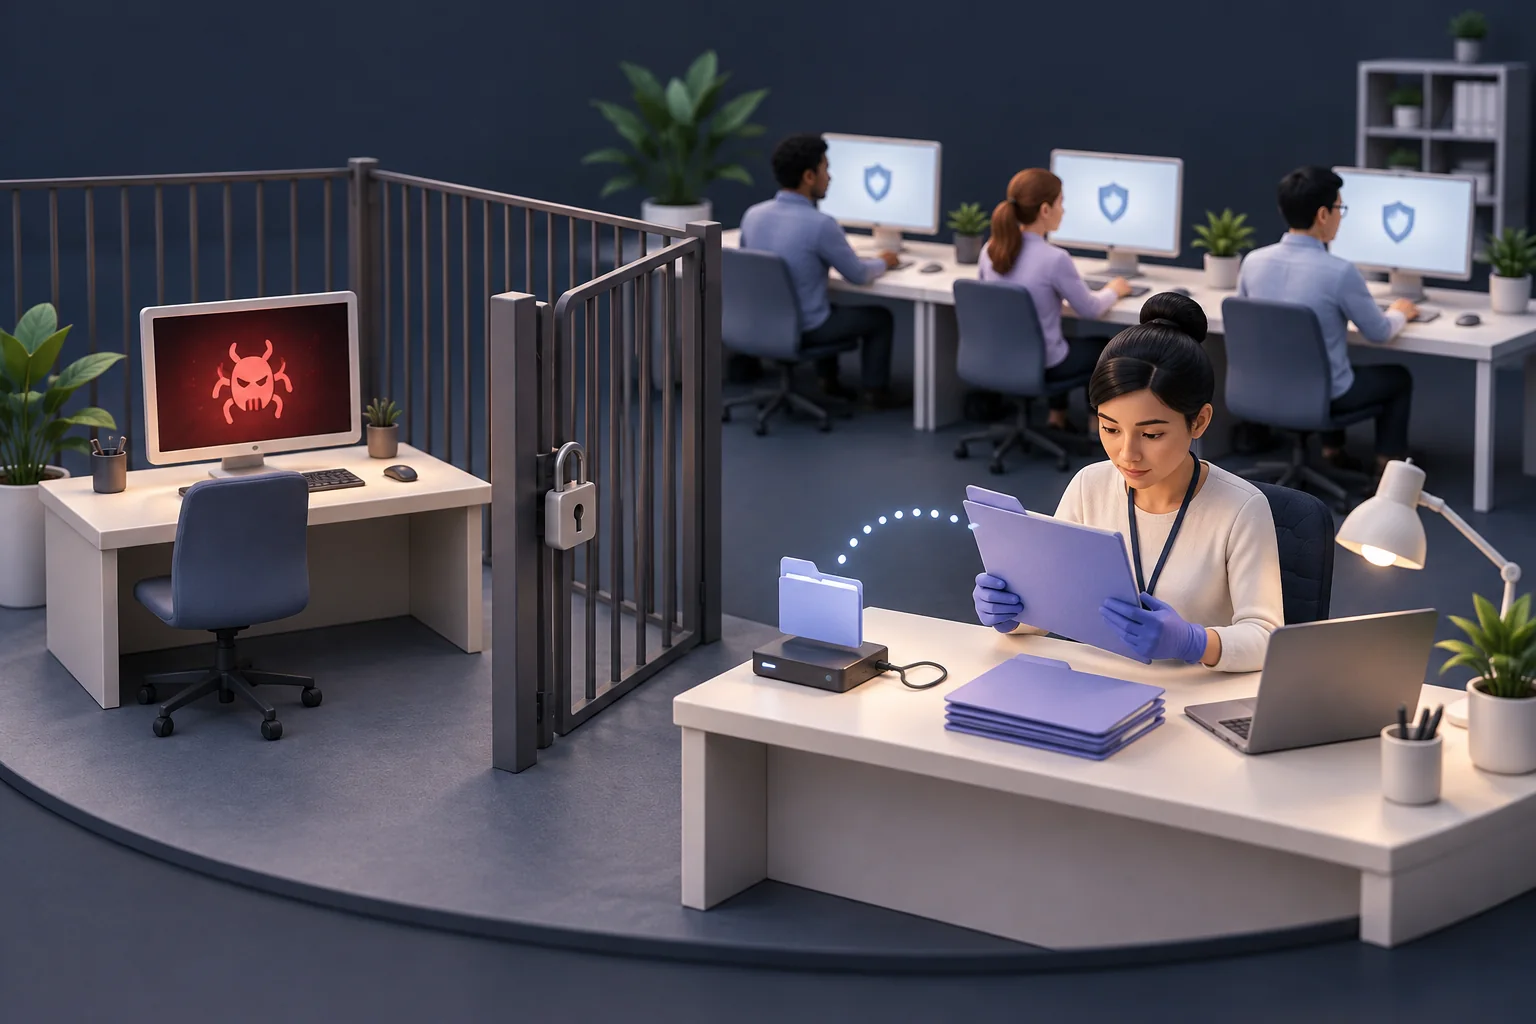
Incident response is a coordinated way to handle a suspected or confirmed security event. Reporting early helps the team assess what happened. You do not need to prove the whole incident before asking the right team for help.
Illustrated analogy · Select the image to enlargeWatch it work
A fictional, simplified model. Select a component to inspect it, or follow the steps in order.
Explore the system
Suspicion
A user reports an unusual event.
Read every step without animation
Uncoordinated response
- Suspicion. A user reports an unusual event.
- Evidence deleted. Someone wipes files without coordination.
- Scope uncertain. The team loses useful investigation context.
Act quickly, but use an agreed response process.
Coordinated response
- Triage. Assess affected assets and urgency.
- Contain + investigate. Limit harm while preserving relevant evidence.
- Recover + improve. Validate restoration and address causes.
Response is an ongoing capability, not only an emergency checklist.
Attack view
A responder deletes suspicious files immediately, losing useful evidence while an attacker’s other access remains active.
Defender view
- Define reporting, authority and escalation before an incident.
- Validate scope and recovery; capture lessons and assign improvements afterward.
Common mistakes
- An alert is not automatically a confirmed incident.
- Recovery without closing the access route can lead to recurrence.
Check your understanding
Active recall: explain this idea in 30 seconds
Incident response is a coordinated way to handle a suspected or confirmed security event. Reporting early helps the team assess what happened. You do not need to prove the whole incident before asking the right team for help.
Now give an example and name one limitation. Revisit the explanation if you get stuck.
Primary sources
Original explanations informed by these specifications and official resources. Source versions and lesson review are separate from product updates.
Content reviewed 2026-09-10. Read the editorial policy.